
International Research Journal of Engineering and Technology (IRJET) e-ISSN: 2395-0056
Volume: 13 Issue: 01 | Jan 2026 www.irjet.net p-ISSN: 2395-0072
PROF.

International Research Journal of Engineering and Technology (IRJET) e-ISSN: 2395-0056
Volume: 13 Issue: 01 | Jan 2026 www.irjet.net p-ISSN: 2395-0072
PROF.
ANIK C. NAIK1, PROF. MAYUR G. UHNALE2 , SARTHAK K. PAWAR3 , SAGAR S. SAWANT4 , TUSHAR B. MULE5, SUYOG Y. THOMBRE6 ,
1(HOD, Dept .of Computer Engineering), S.Y.P Shreeyash College Of Engineering And Technology (Polytechnic), Chh.Sambhajinagar, India
2(Prof (Guide) , Dept .of Computer Engineering), S.Y.P Shreeyash College Of Engineering And Technology(Polytechnic), Chh.Sambhajinagar, India
3,4,5,6(Students, Department of Computer Engineering ),S.Y.P Shreeyash College Of Engineering And Technology(Polytechnic), Chh.Sambhajinagar, India
Abstract - In recent years, the rapid growth of cloud-based services and online data sharing has increased the risk of data breaches and cyber-attacks. Traditional file sharing systems often fail to provide adequate security, leading to unauthorized access and data loss. This paper proposes a cyber security–based secure file sharing system that focuses on protecting data confidentiality, integrity, and access control. The proposed system employs user authentication, role-based access control, and encryption techniques to secure files during upload, storage, and transmission. Files are encrypted before being stored on the server, ensuring that data remains protected even in the event of unauthorized access. Secure key management is implemented to allow only authorized users to decrypt shared files. Additionally, the system maintains audit logs to monitor user activities and detect suspicious behavior. Experimental results show that the system effectively prevents unauthorized access while maintaining efficient performance. The proposed solution is suitable for secure file sharing in cloud and organizational environments.
Key Words: Cyber Security, Secure File Sharing, Data Encryption, Access Control, Cloud Security
1. Introduction
Inrecentyears,therapidgrowthofinformationtechnology andinternet-basedserviceshastransformedthewaydatais stored, accessed, and shared. File sharing systems have becomeanessentialcomponentofmoderncommunication, enablinguserstoexchangedocuments,multimediafiles,and sensitive information efficiently across networks. Cloud computing and online storage platforms have further enhancedtheconvenienceoffilesharingbyallowingusers toaccessdata anytimeand fromanywhere.However,this increased accessibility has also introduced significant securityandprivacychallenges.
As the volume of digital data continues to grow, cyber threats targeting file sharing systems have become more frequent and sophisticated. Unauthorized access, data leakage, identity theft, malware attacks, and man-in-themiddle attacks pose serious risks to both individuals and organizations.Traditionalfilesharingmechanismsoftenlack
adequatesecurityfeatures,makingthemvulnerabletosuch attacks. In many cases, files are transmitted or stored withoutproperencryption,allowingattackerstointercept, modify,ormisusesensitiveinformation.
Cyber security plays a crucial role in addressing these challenges by protecting digital assets from unauthorized accessandmaliciousactivities.Itinvolvestheapplicationof technologies,processes,andpracticesdesignedtosafeguard networks,systems,anddata.Keycybersecurityprinciples such as confidentiality, integrity, and availability are essential for ensuring secure file sharing. Confidentiality ensures that data is accessible only to authorized users, integrity guarantees that data remains unchanged during transmission,andavailabilityensuresthatauthorizedusers canaccessdatawheneverrequired.
A cyber security based file sharing system integrates multiple security mechanisms to provide a secure environmentfordataexchange.Encryptiontechniquesare usedtoconvertplaindataintounreadableformatsbefore storageortransmission,ensuringdataconfidentialityevenif itisintercepted.Secureauthenticationmechanismsverify user identities, preventing unauthorized access to the system. Access control policies further restrict file access based on user roles and permissions, reducing the risk of insiderthreatsanddatamisuse.
This paper presents a cyber security based file sharing systemdesignedtoenhancedataprotectionandusertrust. Theproposedsystemfocusesonsecureuserauthentication, encryptedfilestorage,andcontrolledfileaccesstominimize security vulnerabilities. By incorporating cyber security techniquesintothefilesharingprocess,thesystemaimsto provideareliableandsecureplatformfordatasharingover untrustednetworks.Theproposedapproachissuitablefor real-worldapplicationssuchascorporatedatasharing,cloud storage services, educational platforms, and government systems where data security and privacy are of utmost importance.
International Research Journal of Engineering and Technology (IRJET) e-ISSN: 2395-0056
Volume: 13 Issue: 01 | Jan 2026 www.irjet.net p-ISSN: 2395-0072
The primary ideal of the Cyber Security Based train participating System is to give a secure, dependable, and effective platform for participating digital lines over the internet. The system is designed to address the security challengesassociatedwithtraditionaltrainsharingstylesby integratingadvancedcybersecuritymechanisms.
Thespecific objectsoftheproposedsystemareasfollows
To insuresecure stonerauthenticationsothatonly authorized druggiescan piercethe trainsharing system.
To give confidentiality of data by cracking lines before storehouseandtransmission.
To maintain data integrity by precluding unauthorized revisionof linesduringtransferor storehouse.
To apply access control mechanisms that circumscribe train access grounded on stoner placesand warrants.
To coverthesystemagainstcommoncyber-attacks similar as unauthorized access, data interception, andmalware pitfalls.
To enable secure train upload, download, and participatingwith minimumperformanceoutflow.
Toenhance stonertrustanddata sequestrationin pall and network- grounded train sharing surroundings.
By achieving these objects, the proposed system aims to deliverarobustcybersecurity resultthatsupportssafeand effective train sharing for associations and individual druggies.
ThemethodologyoftheCyberSecurityBasedFileSharing System focuses on designing and implementing a secure frameworkforstoringandsharingfilesoveranetwork.The proposedmethodologyintegratescybersecuritytechniques such as authentication, encryption, and access control to ensure secure data handling throughout the file sharing process. The system follows a structured approach that includesuserregistration,secureauthentication,encrypted file storage, controlled file access, and secure file transmission.
Initially, users are required to register in the system by providingvalidcredentials.Duringregistration,userdetails aresecurelystoredinthedatabaseusinghashingtechniques to protect sensitive information such as passwords. Once registered, users must authenticate themselves through a secureloginprocess.Onlyauthenticatedusersaregranted access to system functionalities, which helps prevent unauthorizedentry.
Aftersuccessfulauthentication,userscanuploadfilestothe system. Before storing any file on the cloud or server, the systemappliesencryptionalgorithmstoconverttheoriginal file into encrypted form. This ensures that even if unauthorized access occurs at the storage level, the data remains unreadable. The encrypted files are then stored securelyonthefilestorageserver.
When a user requests to download or access a file, the system verifies the user’s access rights using an access control mechanism. Role-Based Access Control (RBAC) is appliedtoensurethatuserscanaccessonlythosefilesfor whichtheyhavepermission.Uponsuccessfulauthorization, theencryptedfileisretrievedfromthestorageserverand decryptedbeforebeingdeliveredtotheuser.
Tomaintaindataintegrity,hashingtechniquesareusedto verifythatthefilehasnotbeenalteredduringtransmission. Secure communication protocols are employed to protect datawhileitisbeingtransferredbetweentheuserandthe server. This step-by-step methodology ensures confidentiality,integrity,andavailabilityofdatawithinthe filesharingsystem.
Overall, the proposed methodology provides a systematic andsecureapproachtofilesharingbyintegratingmultiple cybersecuritymechanisms,makingthesystemreliableand suitableforreal-worldsecuredatasharingapplications.
Withtherapidadvancementofinformationtechnologyand thewidespreaduseoftheinternet,digitaldatahasbecome one of the most valuable assets for individuals and organizations.Largevolumesofsensitiveinformationsuch as personal data, financial records, and confidential documents are stored and transmitted through online platforms. This increasing dependence on digital systems has also led to a significant rise in cyber threats, making cybersecurityacriticalrequirementinmoderncomputing environments.
Traditional systems often lack adequate security mechanismstoprotectdatafromunauthorizedaccessand malicious attacks. Cyber threats such as hacking, data breaches, malware infections, phishing, and man-in-themiddle attacks can result in data loss, privacy violations, financial damage, and reputational harm. In file sharing
International
Volume: 13 Issue: 01 | Jan 2026 www.irjet.net p-ISSN: 2395-0072
systems,theriskisevenhigherbecausedataisfrequently transmittedoverpublicanduntrustednetworks. Cyber security is essential to ensure the confidentiality, integrity, and availability ofinformation.Confidentiality preventsunauthorizedusersfromaccessingsensitivedata, integrityensuresthatdataisnotalteredduringstorageor transmission, and availability guarantees that authorized userscanaccessdata wheneverrequired. Withoutproper cyber security measures, these fundamental principles cannotbemaintained.
In cloud-based and online file sharing systems, cyber security techniques such as encryption, authentication, accesscontrol,andsecurecommunicationprotocolsplaya vitalroleinprotectingdata.Encryptionsafeguardsdataby convertingitintoanunreadableformat,whileauthentication andaccesscontrolrestrictsystemaccesstoauthorizedusers only.Thesemechanismssignificantlyreducetheriskofdata misuseandcyber-attacks.
Therefore, the need for cyber security has become more criticalthaneverinordertoprotectdigitalassets,maintain user trust, comply with data protection regulations, and ensuresecureandreliablesystemoperation.Implementing strongcybersecuritymeasuresisessentialforthesuccessful deploymentofsecurefilesharingsystemsandothermodern digitalapplications.
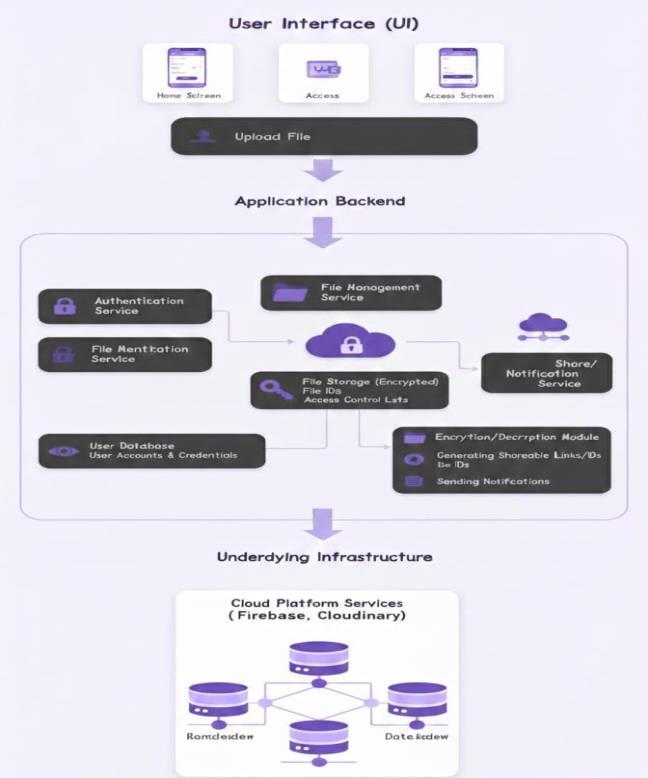
The proposed Cyber Security Based File Sharing System followsalayeredandmodulararchitecturetoensuresecure, efficient,andreliablefilesharing.Thearchitectureisdivided into three main layers: User Interface (UI), Application Backend,and Underlying Infrastructure.Eachlayerplays asignificantroleinmaintainingsystemsecurity,scalability, andperformance.
The User Interface (UI) layerrepresentsthefront-endof the system through which users interact with the application. It includes screens such as the home screen, accessscreen,andfileuploadinterface.Userscansecurely log in, access their dashboard, and upload files using this interface.Alluserrequestsareforwardedtothebackendfor furtherprocessing.
The Application Backend layer is the core of the system wheremajorsecurityandfilemanagementoperationsare performed. It consists of multiple services that work togethertoprovidesecurefilesharing.The Authentication Service verifies user credentials and ensures that only authorized users can access the system. The File Management Service handles file upload, download, and sharingoperations.Beforestorage,filesareprocessedbythe File Encryption Service, which encrypts data to protect confidentiality.
Encrypted files are stored in the File Storage Module, where file identifiers and access control lists (ACLs) are maintained.Thisensuresthatfilescanonlybeaccessedby users with proper permissions. The Access Control Mechanism enforces role-based permissions to prevent unauthorized access. Additionally, the Encryption/Decryption Module manages cryptographic operationsandgeneratessecureshareablefilelinksorIDs. The Share/Notification Service isresponsibleforsending notificationstouserswhenfilesaresharedoraccessed. User-related information such as account details and credentials is securely maintained in the User Database, further enhancing system security. All communication between modules is performed using secure channels to preventdatainterceptionandtampering.
The Underlying Infrastructure layerprovidesthecloudbased support required for storage and processing. Cloud platformservicessuchasFirebaseandCloudnaryareused forscalablestorage,databasemanagement,andsecuredata handling.Thislayerensureshighavailability,faulttolerance, andefficientresourcemanagement.
Overall,thesystemarchitectureintegratesauthentication, encryption,accesscontrol,andcloudservicestoprovidea secureandreliablefilesharingenvironment.Byenforcing securityateverylayer,theproposedarchitectureeffectively protects data confidentiality, integrity, and availability, makingitsuitableforreal-worldcybersecurityapplications.
2395-0056
Volume: 13 Issue: 01 | Jan 2026 www.irjet.net p-ISSN: 2395-0072
The working of a secure file-sharing system that uses authentication and encryption to protect user data. The processstartswhentheuserclicksthesign-inoption,which opens the Google OAuth authentication form. The system usespass word.authenticate()toverifytheuser.Theuser enters an email and password, and the system checks whetherthelogincredentialsarecorrect.Ifthecredentials areinvalid,anerrormessageisshownandtheuserisasked tore-enterthedetails.Ifthecredentialsarevalid,theuser successfullylogsintothedashboard.Afterloggingin,theuser isgivenanoptiontoencryptthefile.Ifencryptionisselected, thefileisencryptedusingapasswordtoensuredatasecurity. Theusercanthenchoosewhethertostorethefileorshareit. Ifthefileisstored,itissecurelyuploadedtostorage.Ifthefile isshared,asharablelinkisgeneratedanddisplayedthrough a chat client popup, along with the password required to access the file. The receiver can decrypt the file using the shared password. Finally, after completing the required actions,theuserlogsout,andtheprocessends.
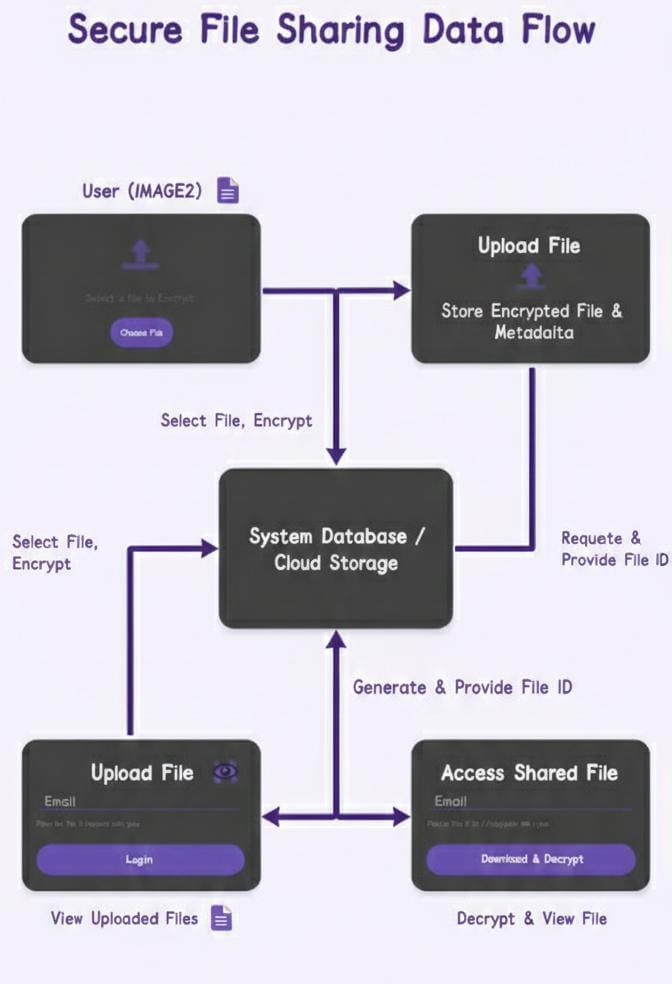
TheSecureFileSharingData FlowDiagramillustratesthe flow of data within the cyber security based file sharing systemfromfileuploadtosecureaccessbyauthorizedusers. Thediagramhighlightshowencryption,storage,andaccess controlmechanismsareappliedateachstagetoensuredata confidentialityandsecurity.
Initially,the User selectsafilefromthelocalsystemthrough the user interface. Before uploading, the selected file is processed by the system and encrypted to prevent unauthorizedaccess.Thisencryptedfileisthenforwardedto the Upload File module, which handles the secure transmissionofdatatothebackendsystem.
The encrypted file along with its associated metadata is storedinthe System Database / Cloud Storage.Metadata includes information such as file identifiers, ownership details,andaccesspermissions.Storingonlyencryptedfiles inthedatabaseensuresthatdataremainsprotectedevenif thestoragesystemiscompromised.
Aftersuccessfulstorage,thesystemgeneratesaunique File ID fortheuploadedfile.ThisFileIDisprovidedtotheuser andisusedasasecurereferenceforaccessingorsharingthe file.Whenauserrequeststoaccessasharedfile,thesystem verifies the request using the provided File ID and checks accesspermissions.
Authorizeduserscanviewtheiruploadedfilesthroughthe View Uploaded Files interface.Whenanaccessrequestis approved, the encrypted file is retrieved from the cloud storage and passed to the Access Shared File module. At thisstage,thesystemperformsdecryptiontoconvertthefile backintoitsoriginalformat.
Finally,thedecryptedfileisdeliveredtotheauthorizeduser forviewingordownloading.Throughoutthisprocess,secure communicationandaccesscontrolmechanismsensurethat onlyauthenticateduserscanupload,access,orsharefiles. Thisstructureddataflowensuressecurefilehandlingwhile maintainingsystemefficiencyandreliability.
Inthispaper,aCyberSecurityBasedFileSharingSystemhas beenpresentedtoaddressthegrowingsecuritychallenges associatedwithtraditionalfilesharingplatforms.Withthe increasinguseofcloudservicesandonlinedataexchange, protectingsensitiveinformationfromunauthorizedaccess and cyber threats has become essential. The proposed systemfocusesonenhancingdataconfidentiality,integrity, and secure accessibility through the integration of cyber securitymechanisms.
The system architecture incorporates secure user authentication, file encryption, controlled access, and encryptedcloudstoragetoensurethatfilesareprotectedat everystageofthesharingprocess.Byencryptingfilesbefore storageandtransmission,thesystemminimizestheriskof data leakage even if the storage infrastructure is compromised.Theuseofaccesscontrolmechanismsensures thatonlyauthorizeduserscanupload,access,orsharefiles, therebyimprovingoverallsystemreliabilityandtrust.
International Research Journal of Engineering and Technology (IRJET) e-ISSN: 2395-0056
Volume: 13 Issue: 01 | Jan 2026 www.irjet.net p-ISSN: 2395-0072
The data flow analysis demonstrates that the proposed approach efficiently manages secure file upload, storage, sharing, and retrieval while maintaining system performance. The modular design of the system makes it scalableandadaptableforvariousreal-worldapplications suchascorporatedatasharing,educationalplatforms,and cloud-basedstorageservices.
Inconclusion,thecybersecuritybasedfilesharingsystem provides a secure and effective solution for modern file sharingrequirements.Futureenhancementsmayincludethe integrationofmulti-factorauthentication,blockchain-based access management, and advanced intrusion detection techniques to further strengthen system security and resilienceagainstemergingcyberthreats.
1. William Stallings, Cryptography and Network Security Principles and Practice, 7th Edition, PearsonEducation,2017.
2. Atul Kahate, Cryptography and Network Security, 3rdEdition,McGraw-HillEducation,2018.
3. Behrouz A. Forouzan, Data Dispatches and Networking,5thEdition,McGraw-Hill,2013.
4. NIST, “ companion to Cyber Security, ” National Institute of norms and Technology, NIST Special Publication800-53and800-171.
5. Subashini and V. Kavitha, “ A Survey on Security Issues in Service Delivery Models of Cloud Computing, ” Journal of Network and Computer Applications,vol.34,no.1,pp.1–11,2011.
6. Armbrust et al., “ A View of Cloud Computing, ” Dispatches of the ACM, vol. 53, no. 4, pp. 50 – 58, 2010.
7. Sahai and B. Waters, “ Fuzzy Identity- Grounded Encryption, ” Advances in Cryptology –EUROCRYPT,Springer,2005.
8. Rivest, A. Shamir, and L. Adleman, “ A system for carrying Digital Autographs and Public- Key Cryptosystems,”DispatchesoftheACM,vol.21,no. 2,pp.120–126,1978.
9. Boneh and M. Franklin, “ Identity- Grounded EncryptionfromtheWeilPairing,”SIAMJournalof Computing,vol.32,no.3,pp.586–615,2003.
10. OWASP Foundation, “ OWASP Top 10 – Web operation Security pitfalls, ” OWASP Documentation,2021.
11. Ren,C.Wang,andQ.Wang,“SecurityChallengesfor thePublicCloud,”IEEEInternetComputing,vol.16, no.1,pp.69–73,2012.
12. Buyya, C. Yeo, and S. Venugopal, “ requestacquainted Cloud Computing Vision, Hype, and Reality, ” Future Generation Computer Systems, Elsevier,2009.
13. MellandT.Grance,“TheNISTDefinitionofCloud Computing, ” NIST Special Publication 800- 145, 2011.
PROF.ANILNAIK
HOD,Dept.ofComputerEngineering
S.Y.PShreeyashCollegeofEngineeringandTechnology (POLYTECHNIC)
PROF.MAYUR.G.UHNALE
GuideDept.ofComputerEngineering
S.Y.PShreeyashCollegeofEngineeringandTechnology (POLYTECHNIC)
MR.SARTHAK.K.PAWAR
PursuingPoly(Co)
S.Y.PShreeyashCollegeofEngineeringandTechnology (POLYTECHNIC)
MR.SAGAR.S.SAWANT
PursuingPoly(Co)
S.Y.PShreeyashCollegeofEngineeringandTechnology (POLYTECHNIC)
MR.TUSHAR.B.MULE
PursuingPoly(Co)
S.Y.PShreeyashCollegeofEngineeringandTechnology (POLYTECHNIC)
MR.SUYOG.Y.THOMBRE
PursuingPoly(Co)
S.Y.PShreeyashCollegeofEngineeringandTechnology (POLYTECHNIC)